
HIPAA telehealth rules protect the health information a licensed provider creates, sends, or stores during your virtual visit, whether that’s a video call, a chat message, or your after-visit summary. The catch: once that information leaves your provider’s system and lands in an app that isn’t a “covered entity” or “business associate,” HIPAA generally stops watching it. That’s why protecting your privacy during telehealth is a two-person job. Your provider secures their side, and you have a role in securing yours.
TL;DR:
- Most HIPAA protections apply only during the telehealth session and do not follow your data once it leaves your provider’s system into third-party apps.
- Protect your privacy by using a private space, headphones, your own device, and avoiding public Wi-Fi during virtual visits.
- Ask your provider if their telehealth platform is HIPAA-compliant and whether they have a signed agreement with the vendor to ensure your data is adequately protected.
- Carefully consider where your session recordings and health records are stored, how long they are kept, and who has access, especially if exported to third-party apps.
- Be vigilant about suspicious links, unverified apps, public Wi-Fi, and always confirm privacy policies and security measures before sharing sensitive health information digitally.
Table of Contents
- What HIPAA Telehealth Rules Actually Cover
- Your Rights During and After a Virtual Visit
- How to Protect Your Privacy During a Telehealth Visit
- Third-Party Apps, Recordings, and Where HIPAA’s Protection Ends
- Red Flags and Questions Worth Asking Your Provider
- Why Shared Responsibility Beats Blind Trust
- Learn More About Chameleon Healthcare’s Telehealth Privacy Approach
- Sources
What HIPAA Telehealth Rules Actually Cover
HIPAA protects what’s called protected health information, or PHI. When that information travels electronically, like during a video visit, it’s called ePHI. If you’re seeing a licensed provider through a telehealth platform, nearly everything from that appointment counts: the video itself, your symptoms as you describe them, the notes your provider types, and the treatment plan that follows. This is confirmed under the Privacy Rule’s national standards, which require covered providers to protect your information and tell you how it’s used.
You should reasonably expect a few technical safeguards from any covered provider: encryption while your session data travels between your device and theirs, some form of login authentication, and access controls so random staff can’t casually browse your file. Whether these rules apply depends partly on how you connect. A phone call over a standard landline sits outside the Security Rule’s electronic-transmission requirements, but audio-only visits made through VoIP apps or mobile platforms do fall under it, according to OCR’s audio-only telehealth guidance. Either way, most providers now treat every telehealth format the same and secure it accordingly.
Your Rights During and After a Virtual Visit
Before your first appointment, you should receive a Notice of Privacy Practices. It’s not paperwork to skim past. This notice spells out how your provider collects, uses, and shares your information, and it should specifically address how telehealth sessions and recordings fit into that picture.
You also have the right to access and get copies of your own ePHI, and you can direct your provider to send those records to a third-party app of your choosing; understanding teleradiology state licensing: how coverage works can clarify where your data may be stored and how state-level rules apply. Here’s where it gets tricky: once you make that choice, HIPAA’s protections generally stop following the data. The app you picked isn’t bound by the same rules your provider is.
You can also ask for confidential communications (a different phone number, a specific email), and you’re entitled to ask exactly who can access any recording or stored session data tied to your visit. If your provider experiences a breach involving your PHI, the Breach Notification Rule sets firm timelines for telling you. If you believe your privacy rights were violated, you can file a complaint directly with the HHS Office for Civil Rights.
How to Protect Your Privacy During a Telehealth Visit
Your provider can build every safeguard correctly and your privacy can still slip if your setup at home works against you. A private, prioritized checklist helps more than a vague sense that you “should be careful.”
- Pick a truly private space. A closed room, or even a parked car, beats a kitchen table where family or coworkers can hear your symptoms.
- Wear headphones and angle your screen. This keeps both audio and visuals away from anyone nearby.
- Use your own device, not a shared or work-issued one. Employer-managed laptops often come with monitoring software you didn’t sign up for.
- Skip public Wi-Fi entirely. Coffee shop and airport networks are common entry points for intercepted traffic.
- Turn on multi-factor authentication wherever your provider’s platform offers it, and keep your device software updated.
- Mute or unplug smart speakers and cameras in the room before your appointment starts.
- Delete session recordings or files you don’t need to keep, and clear them off shared devices.
- Double-check any link your provider sends before clicking. If it looks off, call the office directly to confirm.
HHS’s own guidance backs nearly every item here, right down to the recommendation to use a private location and unique passwords. A detailed privacy tips PDF from HHS adds the smart-speaker and public Wi-Fi warnings specifically.
Pro Tip: Keep a simple habit: log out of the telehealth platform completely after your visit instead of just closing the browser tab. Session data can linger in an open tab longer than you’d expect, especially on shared or work devices.
Third-Party Apps, Recordings, and Where HIPAA’s Protection Ends
Not every app your provider uses, or that you use to store your own records, is bound by HIPAA. A platform your provider contracts with directly, and that signs a business associate agreement, has to follow the same rules your provider does. A consumer health app you downloaded on your own, unconnected to that agreement, usually doesn’t.
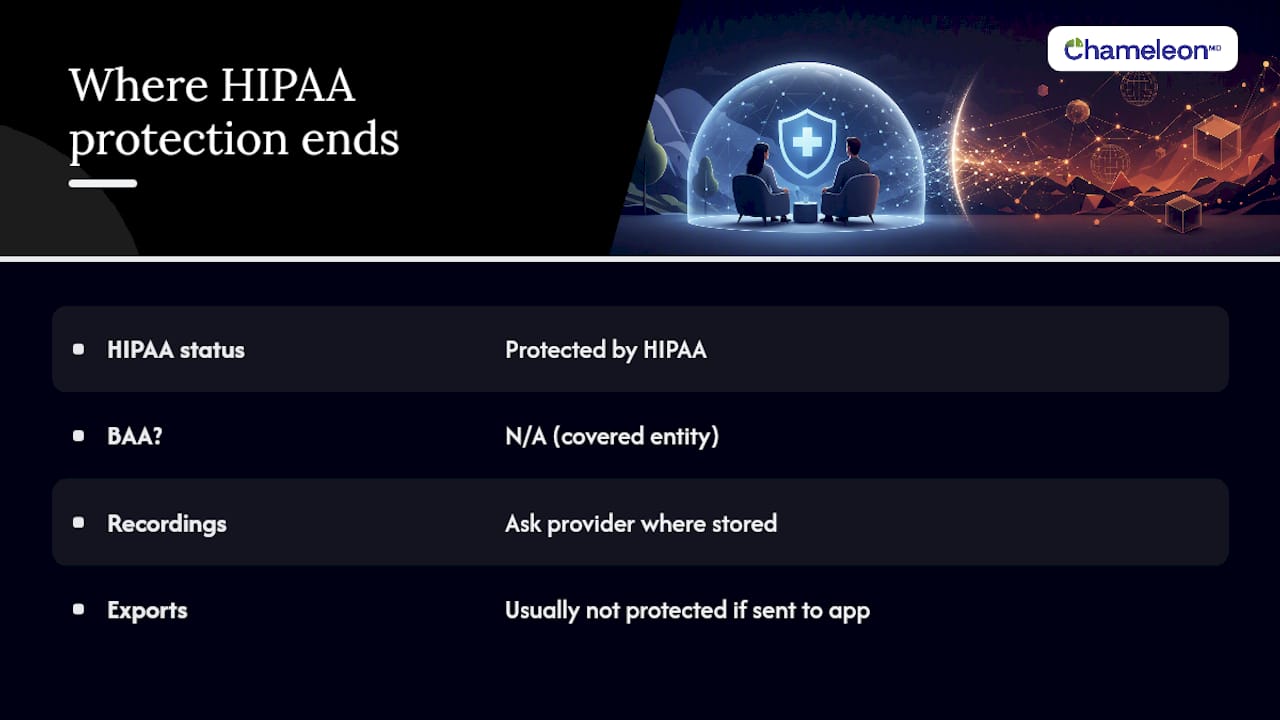
This distinction matters most with recordings and records exports. ONC’s consumer guidance puts it plainly: HIPAA protects information held by covered entities, but not information you voluntarily hand to a third-party app outside that relationship. If you export your visit summary to a fitness tracker or a personal health folder app, ask yourself whether that app is even subject to HIPAA before you send anything sensitive.
Before your visit, it’s worth asking your provider directly whether a business associate agreement exists with their telehealth vendor, and where any recording or transcript actually lives once the call ends.
Red Flags and Questions Worth Asking Your Provider
A short list of direct questions can tell you more about a provider’s privacy practices than any privacy policy buried in fine print.
- Is this telehealth platform HIPAA-compliant, and do you have a signed agreement with the vendor?
- Where is my session recording stored, and for how long?
- Who, specifically, can access my recording or transcript?
- Is multi-factor authentication required for staff accessing my file?
- What happens, step by step, if there’s a data breach involving my information?
Watch for warning signs, too: links from unfamiliar senders, a provider asking you to use a public consumer app with no visible privacy controls, or any suggestion that you take the call over public Wi-Fi. If something feels off after a visit, contact your provider first, request a copy of your records, and file a complaint with OCR if the response doesn’t satisfy you.
Why Shared Responsibility Beats Blind Trust
Most patients assume HIPAA is a wall that automatically protects everything tied to their health. It isn’t. It’s a set of obligations on covered providers, and it has real gaps the moment you introduce an app or a device HIPAA was never built to cover. HHS itself frames privacy in telehealth as a shared responsibility between provider and patient, and that framing gets underused in most consumer advice.
The overlooked nuance is control, not just protection. You can request that certain details be withheld from shared communications, and you can insist on knowing exactly where a recording sits and who can open it. Providers have to respond to those requests. Most patients never ask.
— Vector
Learn More About Chameleon Healthcare’s Telehealth Privacy Approach
Our telehealth model is built around the shared-responsibility idea: transparent pricing, no insurance friction, and clear expectations about how your virtual visit works from the moment you log in. If you’re weighing telehealth options and want practical guidance on securing your end of the visit, our guide to protecting your online healthcare privacy walks through device and connection choices in more detail, and our virtual care setup guide covers what to expect technically before your first appointment.
If you’re dealing with something common, like a sprain, reflux, or a tooth infection flaring up at an inconvenient hour, same-day virtual care with upfront pricing can provide a convenient alternative to an ER trip. Review Chameleon Healthcare’s plans to see membership and single-visit pricing side by side, or reach out to support directly with any privacy questions before you book your first visit.
This article is general information, not a substitute for advice from a qualified doctor. Consult a qualified healthcare professional about your own circumstances before acting on anything here.